Patch Management agent status
NAVIGATION Modules > Patch Management > Agent Status
PERMISSIONS All users
From the Agent Status page, you can view the patch policy assignment status for all of the endpoints in your environment. You can also manage and manually run assigned policies for individual devices.
This article describes the page's layout and functions.NOTE For a comprehensive overview of how profiles and policies work in VSA 10, refer to Policies overview. To learn how to automate your patch review process, consult Automating patch review.
Overview
From the left navigation menu in VSA 10, navigate to Patch Management > Agent Status.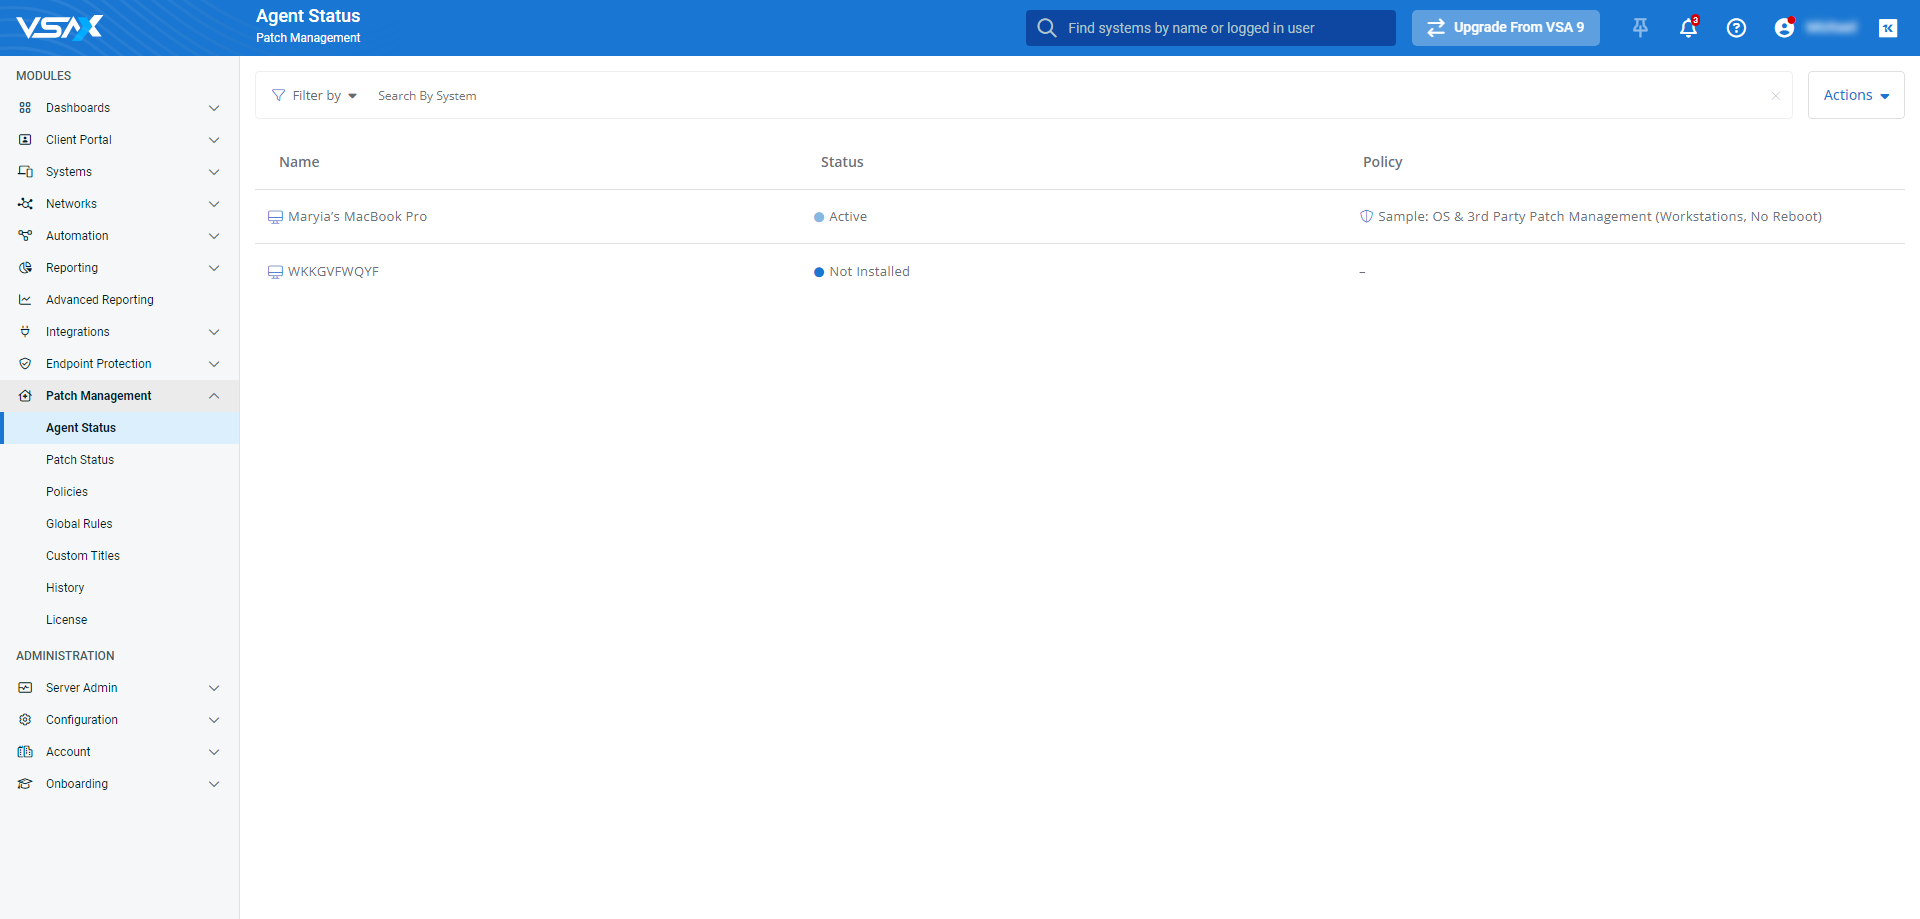
Agent Status values
Devices will display their Agent Status as one of the following:
- Not Installed: No patch management policy is assigned to the device.
- Assigning: The policy is being applied and has not finished.
- Active: The assigned policy is applied and being enforced on the device.
- Checking: A policy run is in progress and the agent is evaluating the device against the policy to determine which updates apply.
- Installing: A policy run is in progress and the agent is deploying the approve updates.
- Removing: The policy has been removed and is no longer applied.
As you navigate, you'll see the following features and fields:
 Page features
| Feature | Definition | |||||
|---|---|---|---|---|---|---|
| Search field | Enter a partial or whole value to filter current view to matching records | |||||
| Filter by | Click to select additional criteria by which you can refine your search | |||||
Actions | Provides actions you can take for the selected device; available options are:
|
Device table| Field | Definition | ||||||||
|---|---|---|---|---|---|---|---|---|---|
| Name | Assigned hostname of the endpoint | ||||||||
| Status | Indicates the installation status and enforcement of the selected policy on the device. | ||||||||
| Policy | Name of the policy assigned to the endpoint | ||||||||
Actions | Move your mouse over any list entry to reveal the following options::
|


How to...
Assign a policy to one or multiple devices
From the Agent Status page, perform the following steps:
To assign a policy to all devices in the current view that do not currently have one , click Actions at the top of the page. Then, click Assign Policy.
To assign a policy to an individual device, move your mouse over its list entry and click the
 icon.
From the drop-down list that appears, select a policy to assign to the chosen devices. Then, click Assign Policy.
You'll see the new policy go into effect for each device with an initial status of Active. Any issues encountered in the deployment process, such as failures to run the policy, will appear in the Status column.


